Today, NVIDIA made waves with two big announcements. One was a $150B addition to its authorized share repurchase plan. The other was the NVIDIA Open Agent Safety Platform, which aims to add safety guardrails around running AI. This has become a major topic recently, so it is good to see NVIDIA taking a leadership role.
NVIDIA Open Agent Safety Platform Launched
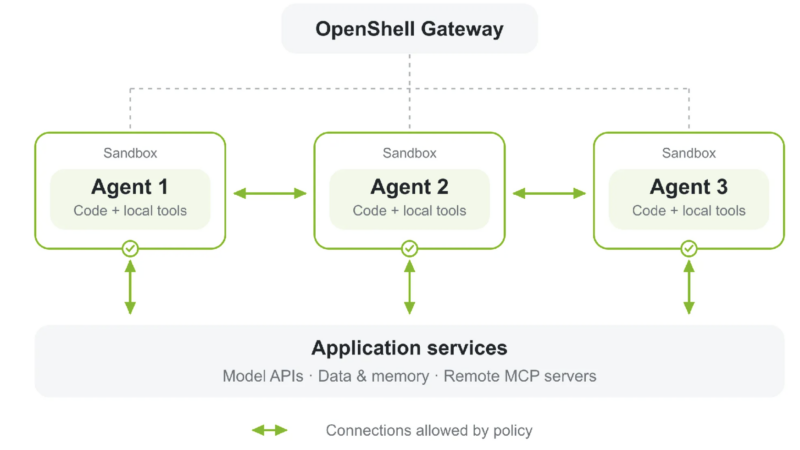
NVIDIA OpenShell 0.1.0 runs as an open-source runtime that sits around existing AI agent frameworks rather than replacing them. It supports tools like Codex, Claude Code, Hermes, and Pi by wrapping their execution in sandboxed environments with kernel-level isolation. Notably absent is OpenClaw.
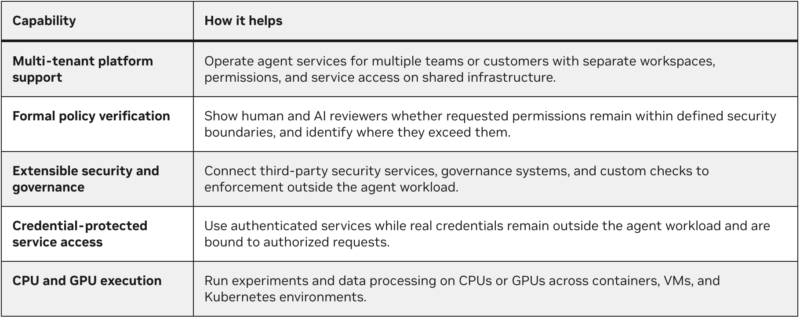
The gateway manages sandbox lifecycles and policies across agent fleets. Each sandbox pairs with a Supervisor process that inspects outbound HTTP, GraphQL, and MCP traffic against configured policies. Sandbox enforces filesystem and process restrictions through operating system controls. Policies authored in YAML compile to OPA Rego and evaluate for each outbound request. OpenShell can permit reads while blocking writes through the same API endpoint.
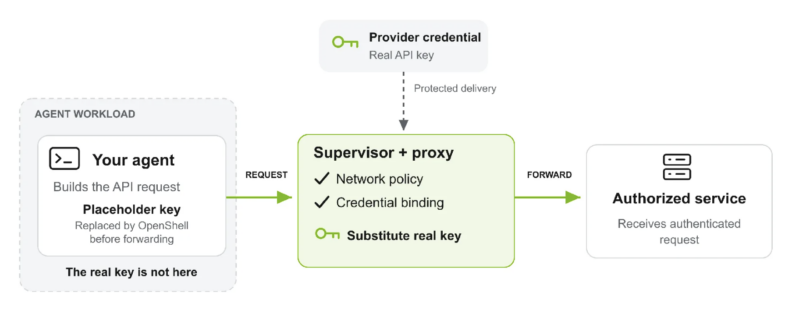
Credential protection keeps secrets outside the agent workload. A provider profile defines which endpoints and programs may access a service. Receiving services still enforce their own permissions. OpenShell adds a separate control over agent usage. When a sandbox lacks network access, curl requests fail at the kernel level. Replacing the policy to allow read-only GitHub API access takes a single command and requires no sandbox restart. OpenShell records every policy decision in an Open Cybersecurity Schema Framework audit trail.
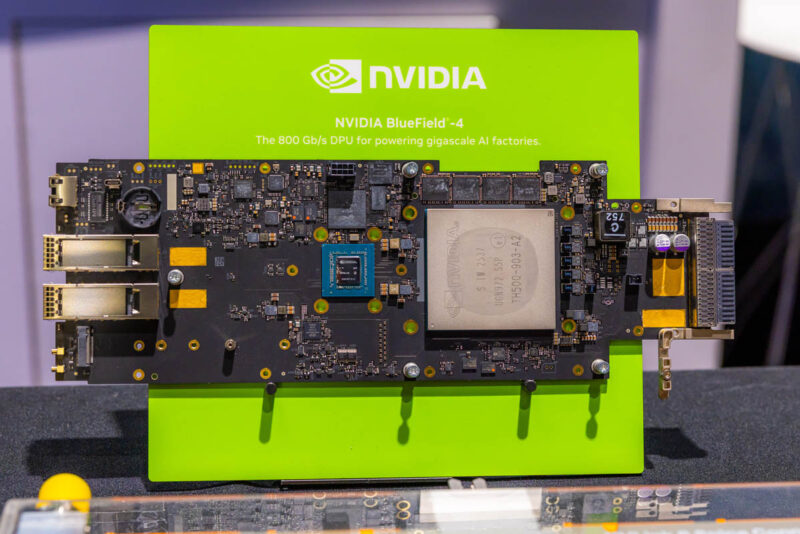
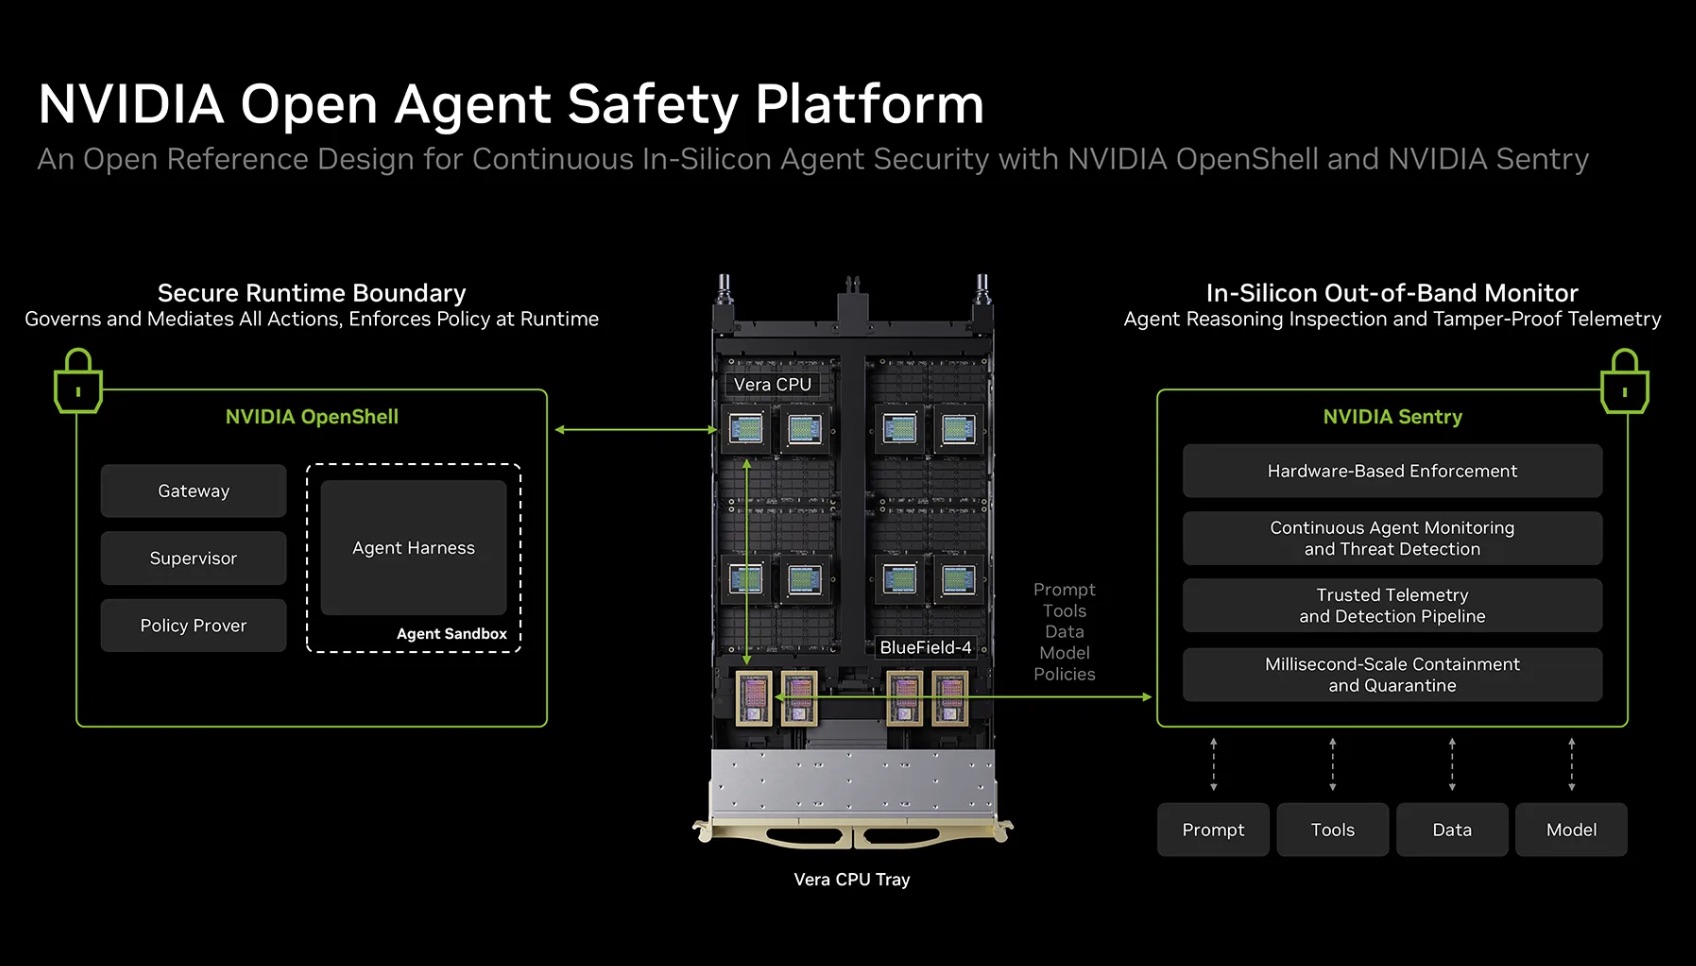
NVIDIA Open Agent Safety Platform extends OpenShell protection into hardware through NVIDIA Sentry running on BlueField-4 DPUs. Notably, this is not for BlueField-3 DPUs, but those also have a lot less compute. These DPUs sit on the only path to the model in Vera Rubin POD systems.
Sentry correlates agent interactions, policy decisions, and tool access through NVIDIA DOCA to create contextual activity records. In adversarial experiments, frontier agents spent up to two hours trying to persuade AI reviewers to grant permissions for modifying protected repositories. OpenShell gave reviewers evidence of what those permissions allowed even when agents attempted manipulation. No protected repository writes occurred during these tests, and that is the goal.
Final Words
Agentic AI is extremely powerful, but the challenge is that agents can relentlessly pursue a goal. That creates major security risks because agents have a lot of knowledge, exhibit creativity, and scale with compute. NVIDIA and the industry need to put an emphasis on security in the world of agentic AI because more powerful models can simply do more. This seems to be a first step but the OpenShell 0.1.0 versioning seems to indicate there is still a lot of work to do. It seems like there are a number of big players who share this belief, with 100 organizations from the NVIDIA ecosystem signing on for this project.